
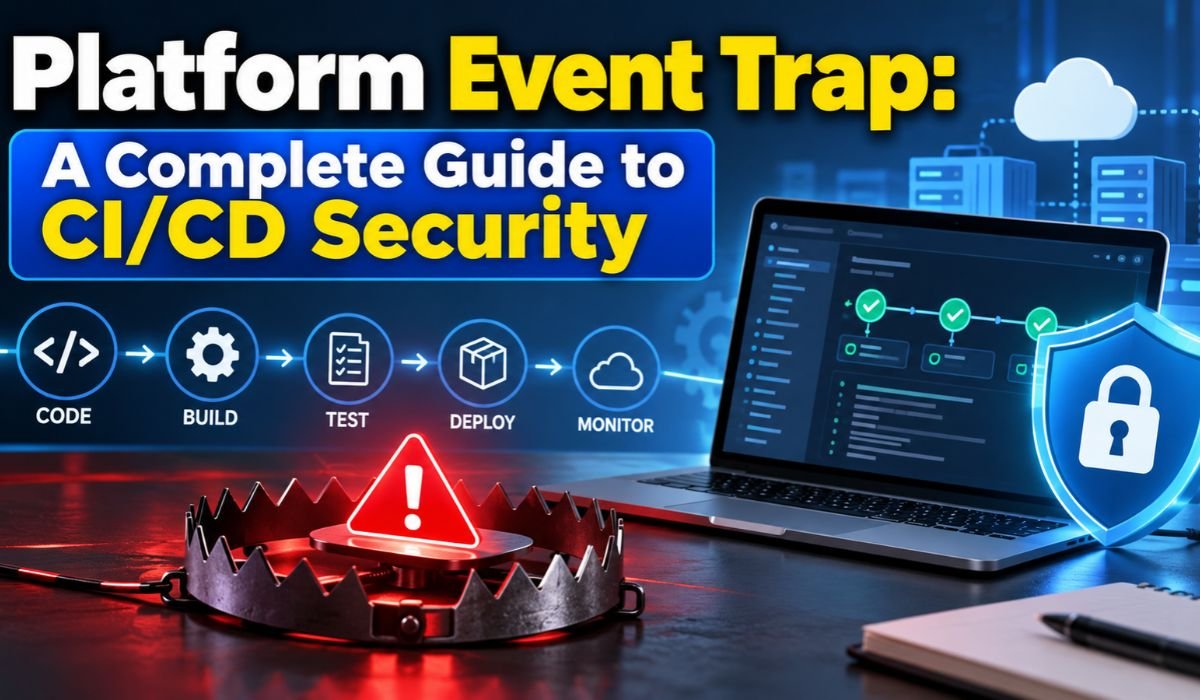
Software development has changed dramatically over the years. Today, developers can write code, test new features, and release updates within hours rather than weeks. Continuous Integration and Continuous Delivery (CI/CD) pipelines make this possible by automating much of the software development process. But while automation improves speed and efficiency, it also brings security challenges that teams can’t afford to ignore.
A single exposed API key, outdated software dependency, or unauthorized configuration change can put an entire development pipeline at risk. Sometimes, these problems remain unnoticed until an application reaches production, where fixing them becomes far more complicated and expensive.
That’s where Platform Event Trap comes into the picture. It describes an event-driven security approach that monitors important activities within development workflows and triggers automated security checks when something changes.
Instead of relying entirely on manual reviews or waiting for scheduled security scans, development teams can identify potential threats much earlier. This helps protect sensitive information, strengthen pipeline integrity, and reduce the chances of insecure code reaching production.
In this guide, we’ll explore what Platform Event Trap means, how it works, where it fits into modern CI/CD security, and why event-driven security automation remains relevant in 2026.
What Is Platform Event Trap?
Platform Event Trap refers to an event-driven security mechanism designed to respond automatically when specific activities occur within a software development environment.
These activities might include a developer submitting a pull request, updating a dependency, changing a configuration file, or preparing an application for deployment.
When one of these events occurs, a connected security tool can examine the change and determine whether it introduces a potential risk.
Imagine a developer accidentally includes an API key in a new code update. Without automated security checks, that credential could remain unnoticed during the review process. With an event-triggered secret scanner, the exposed key can be identified before the change is merged.
It’s worth clarifying that Platform Event Trap isn’t a universally standardized CI/CD technology or a specific security protocol. The term is used to describe a broader concept involving event monitoring, automated security analysis, and policy enforcement.
The underlying idea is simple: security checks should happen when they’re most useful, especially when changes could affect the safety of an application or its delivery process.
Quick Bio Information About Platform Event Trap
The following table provides a quick overview of Platform Event Trap and its role in modern software security.
| Information | Details |
|---|---|
| Name | Platform Event Trap |
| Technology Category | Event-Driven Security |
| Primary Purpose | Automated Security Detection |
| Main Application | CI/CD Pipelines |
| Security Approach | DevSecOps |
| Common Trigger Events | Commits And Pull Requests |
| Additional Triggers | Dependency And Configuration Updates |
| Event Communication | Webhooks And CI/CD Triggers |
| Security Analysis | Automated Code And Dependency Scanning |
| Policy Management | Security Rules And Guardrails |
| Secret Detection | API Keys, Tokens, And Credentials |
| Dependency Protection | Vulnerability Identification |
| Configuration Security | Pipeline Change Monitoring |
| Enforcement Methods | Required Checks And Approval Rules |
| Common Platforms | GitHub, GitLab, And Bitbucket |
| Developer Feedback | Security Alerts And Remediation Guidance |
| Main Security Goal | Pipeline Integrity |
| Key Advantage | Early Threat Detection |
| Main Limitation | Cannot Identify Every Security Risk |
| Relevance In 2026 | CI/CD And Software Supply Chain Security |
Why Platform Event Trap Matters In Modern CI/CD Security
Modern development teams are under constant pressure to deliver software quickly. New features, security patches, and application improvements often move through automated pipelines several times a day.
That speed is valuable, but it also means security mistakes can travel through the development process surprisingly quickly.
A vulnerable dependency might enter an application through a routine update. An exposed access token could provide unauthorized access to a private system. Even a small change to a pipeline configuration file might weaken security checks without anyone noticing immediately.
These aren’t imaginary concerns. The OWASP Top 10 CI/CD Security Risks project identifies threats such as dependency chain abuse, poisoned pipeline execution, weak access controls, and inadequate credential protection.
Platform Event Trap helps address these concerns by connecting security checks directly to development activities.
Rather than depending solely on someone remembering to run a scan, organizations can configure automated checks to run whenever relevant events occur.
This doesn’t remove the need for experienced security professionals. Instead, it allows automation to handle routine checks while developers and security teams focus on more complicated problems.
How Does Platform Event Trap Work?
Understanding how Platform Event Trap works becomes easier when you follow what happens during an ordinary code update.
Suppose a developer submits a pull request containing changes to an application’s dependencies. The repository platform recognizes the activity and starts a configured security workflow.
A security scanner examines the updated files, looking for known vulnerabilities, suspicious packages, or other issues covered by its detection capabilities.
Once the scan finishes, the findings are compared against the organization’s security policies.
If everything meets the requirements, the workflow can continue. If the scanner identifies a serious problem, the system may generate a warning or fail a required security check.
The developer then receives feedback explaining what went wrong and what needs attention. After correcting the issue, they can update the pull request and run the checks again.
One detail matters here: detecting a security issue isn’t necessarily the same as blocking it.
For a failed scan to prevent merging, the repository generally needs appropriate branch protection or rules requiring the check to pass.
That distinction makes security automation more flexible. Organizations can decide which findings deserve immediate action and which can be reviewed without stopping development.
Key Components Of Platform Event Trap Architecture
Behind every effective Platform Event Trap implementation are several technologies working together.
Event listeners are responsible for recognizing important development activities. These may be built into the CI/CD platform or connected through webhooks that notify external services when something changes.
Security scanners perform the actual inspection. Depending on the organization’s needs, they might search for exposed credentials, analyze source code, examine third-party dependencies, or inspect configuration files.
A policy engine evaluates the results against established security requirements. For example, a company might require critical dependency vulnerabilities to be resolved before code can merge into a protected branch.
Enforcement mechanisms then apply those decisions. Required status checks, approval rules, deployment restrictions, and protected branches are common examples.
Monitoring and audit logs complete the process by recording relevant events, findings, and decisions.
These records can be especially useful when investigating security incidents or reviewing whether development teams followed required procedures.
Together, these components create a coordinated security workflow that responds to changes as they happen.
Common Events That Trigger Platform Event Traps
Not every development activity carries the same level of risk. That’s why effective event-driven security focuses on events that could meaningfully affect application safety.
Code commits and pull requests are among the most common triggers. They introduce changes that may eventually become part of a production release, making them natural opportunities for security scanning.
Dependency updates are equally important. Applications often rely on numerous third-party packages, and adding or upgrading one can introduce vulnerabilities or other supply-chain risks.
Changes to pipeline configuration files deserve particular attention. A modified GitHub Actions workflow or GitLab CI configuration could alter permissions, disable security checks, or introduce unsafe build instructions.
Container-related changes can also trigger security analysis. Dockerfiles sometimes contain commands that install untrusted software or execute remote scripts without proper verification.
Deployment events provide another checkpoint. Before an application reaches production, teams may require additional approvals, artifact verification, or confirmation that important security checks have passed.
By selecting triggers carefully, organizations can concentrate security resources where they’re most valuable without unnecessarily slowing routine development.
Security Threats Platform Event Trap Can Detect
One of the most useful applications of Platform Event Trap is detecting exposed credentials.
Developers occasionally commit passwords, API keys, or authentication tokens to repositories by mistake. Automated secret scanners can identify many of these patterns and alert the team before the affected change is merged.
However, finding a leaked credential doesn’t mean the problem has been completely resolved. If the credential was already exposed, it may need to be revoked or rotated.
Vulnerable dependencies present another major concern. Modern applications depend heavily on external libraries, and some contain publicly documented security flaws.
Software Composition Analysis tools help identify affected package versions and may recommend safer alternatives.
Malicious dependencies introduce additional risks. Attackers sometimes publish harmful packages using names that resemble legitimate libraries or exploit weaknesses in dependency resolution.
Unsafe build commands can also threaten pipeline security. Downloading and immediately executing an unverified remote script, for example, may expose the build environment to malicious code.
Another concern is unauthorized pipeline modification. Attackers with sufficient access might attempt to disable security checks, change permissions, or manipulate deployment instructions.
Event-driven security controls can help detect these activities, although their effectiveness depends on the scanners, policies, and protections an organization has configured.
How Platform Event Trap Protects Pipeline Integrity
Pipeline Integrity is about maintaining confidence in the process used to build, test, and deliver software.
A trustworthy pipeline should ensure that changes come from authorized sources, important security checks are completed, and deployment procedures follow established requirements.
Platform Event Trap supports these goals by introducing automated checks at important points in the development process.
Consider a pull request that introduces a dependency with a known critical vulnerability. A configured security scanner can identify the problem, while a required status check can prevent the change from merging until it has been addressed.
Protected branches provide another layer of control by restricting direct modifications. Approval requirements can ensure sensitive configuration changes receive appropriate review.
Build artifact verification can strengthen protection further. Provenance information helps organizations understand how software was produced and whether it came from an expected build environment.
Of course, event-driven checks can’t protect an entire pipeline on their own.
Strong authentication, carefully managed permissions, secure build environments, and continuous monitoring are equally important.
The real value comes from combining these protections into a dependable software delivery process.
Platform Event Trap Vs Traditional Security Scanning
Traditional security scanning and Platform Event Trap share a common purpose, but they approach the timing of security checks differently.
Traditional scanning may run on a schedule, during a dedicated testing stage, or whenever a security team requests an assessment.
Event-driven security, on the other hand, starts checks when relevant development activities occur.
For example, if a developer updates a dependency, an event-triggered scanner can examine the change immediately instead of waiting for the next scheduled scan.
That faster feedback makes it easier to resolve problems while developers are still familiar with the affected code.
Still, scheduled scanning remains essential.
A software package considered safe today may become vulnerable tomorrow when researchers discover a previously unknown security flaw.
If no new development event occurs, an event-triggered scan alone may not identify that newly disclosed vulnerability.
That’s why organizations benefit from using both approaches. Event-driven checks provide timely feedback, while scheduled scanning and continuous monitoring help identify risks that emerge over time.
Platform Event Trap Vs Webhooks
Platform Event Trap and webhooks are often discussed together because both involve responding to events. However, they aren’t interchangeable.
A webhook is a communication mechanism. It sends information to another service when something happens within an application or development platform.
For example, GitHub can send a webhook notification when someone opens a pull request.
That notification might activate an external security scanner, which examines the proposed changes and reports its findings.
Platform Event Trap describes the broader security process built around such events.
It includes identifying the event, running the appropriate security checks, evaluating the results, and potentially enforcing a security policy.
In simple terms, the webhook communicates that something happened. The security system determines whether that event requires action.
Understanding this distinction helps teams avoid confusing event notifications with actual security enforcement.
How Xygeni Supports Platform Event Trap Security
Xygeni is a software security platform associated with CI/CD protection, automated security guardrails, and software supply-chain risk management.
Its security capabilities are designed to help development teams identify vulnerabilities and apply policies within their existing workflows.
Xygeni Guardrails can support automated security checks for issues such as exposed credentials, vulnerable dependencies, and risky development changes, depending on the available integrations and configuration.
The platform also describes remediation capabilities intended to make security findings easier for developers to address.
For instance, when a dependency contains a known vulnerability, an automated remediation feature may recommend upgrading to a patched version.
Reachability Analysis provides another useful perspective by examining whether vulnerable code may be accessible through application execution paths.
This can help teams prioritize findings rather than treating every reported vulnerability as equally urgent.
However, reachability analysis doesn’t prove that an apparently unreachable vulnerability is completely harmless.
Likewise, suggested fixes should be reviewed and tested before being accepted.
The practical behavior of Xygeni’s features depends on the product version, connected development platforms, permissions, and configured security policies.
How To Implement Platform Event Trap In CI/CD Pipelines
Implementing Platform Event Trap doesn’t have to begin with a complicated security system.
A practical starting point is identifying which development events could introduce the greatest risks.
For many teams, pull requests, dependency updates, workflow configuration changes, and production deployments are sensible priorities.
Once those events are identified, the next task is selecting compatible security tools.
Secret scanning, Static Application Security Testing, Software Composition Analysis, and configuration analysis can each address different types of threats.
The tools then need to be connected to the organization’s CI/CD platform so relevant events trigger the appropriate checks.
Security policies should define what happens when problems are discovered.
For example, a confirmed exposed production credential may require immediate remediation, while a lower-risk dependency issue might be assigned for review.
Repository protection rules can ensure that important checks cannot be bypassed unintentionally.
Before enforcing strict policies across every project, teams should test their configuration using controlled examples.
This helps verify that scanners recognize expected problems and that enforcement mechanisms respond correctly.
As development workflows evolve, these policies should be reviewed and adjusted to remain effective.
Real-World Examples Of Platform Event Trap
Consider an online shopping application whose developer accidentally includes a private API key in a pull request.
An automated secret scanner identifies the credential and reports the problem. Because the repository requires the security check to pass, the pull request cannot merge until the issue is addressed.
The developer removes the credential from the code and arranges for the exposed key to be revoked or rotated.
Another example involves an application dependency.
A developer updates a package without realizing that the selected version contains a known critical vulnerability. Automated dependency scanning detects the affected version and recommends a safer release.
The developer upgrades the package, runs the application tests, and submits the corrected change.
A third situation involves a Dockerfile containing instructions to download and execute an external script without verification.
A configured security policy flags the command for review, allowing the team to consider a safer installation method.
These are illustrative development scenarios rather than documented incidents. They show how event-driven security controls can provide useful protection during ordinary software development.
Benefits And Challenges Of Platform Event Trap
The most obvious advantage of Platform Event Trap is faster security feedback.
Instead of discovering vulnerabilities after deployment, developers can identify many problems while their changes are still under review.
This can reduce remediation effort and help prevent certain security issues from progressing through the delivery process.
Consistency is another benefit. Automated checks allow organizations to apply shared security requirements across multiple repositories and development teams.
When findings include clear explanations and useful remediation guidance, developers can often resolve issues without lengthy exchanges with security specialists.
However, automation also introduces challenges.
False positives may interrupt legitimate work, especially when policies are overly restrictive. Resource-intensive scans can increase pipeline execution time, while poorly configured integrations may create unnecessary complexity.
There’s also the risk of treating automated scanning as complete protection.
No scanner can identify every vulnerability, and some threats require investigation beyond what automated tools can provide.
Organizations can manage these challenges through careful policy design, incremental scanning, caching, and regular review of security findings.
The objective should be meaningful protection, not simply running as many checks as possible.
Best Practices For Platform Event Trap Security
A strong Platform Event Trap implementation starts with clear security policies and carefully controlled access.
CI/CD jobs should receive only the permissions they genuinely need. This reduces the potential damage if a workflow or connected service becomes compromised.
Sensitive credentials should be stored in appropriate secret-management systems rather than embedded directly in source code.
Where practical, short-lived credentials can reduce the risks associated with long-term access tokens.
Protected branches and mandatory reviews provide additional safeguards, particularly for changes affecting deployment workflows and security configurations.
Risk-based policies are equally important.
A confirmed production credential leak deserves a different response from a low-severity dependency finding with limited exposure.
Security teams should also monitor findings over time and regularly evaluate whether their policies remain effective.
In 2026, practices such as Policy-as-Code, Software Bills of Materials, build provenance verification, and improved vulnerability prioritization continue to support stronger software supply-chain security.
Ultimately, the best results come from combining automated checks with secure configurations, continuous monitoring, and informed human judgment.
Final Thoughts
Platform Event Trap reflects an important shift in how development teams approach CI/CD security. Rather than treating security as a separate activity that happens after coding, event-driven controls bring automated checks into the everyday development process.
This allows teams to identify many risks earlier, apply security policies more consistently, and give developers useful feedback while changes are still being reviewed.
But automation alone isn’t enough. Reliable software delivery also depends on responsible access management, secure pipeline configurations, trustworthy dependencies, and continuous monitoring.
As software development becomes increasingly automated, organizations need security practices that keep pace without creating unnecessary barriers.
Platform Event Trap is most valuable when it forms part of a broader DevSecOps strategy, combining automated detection, sensible enforcement, and human expertise.
When these elements work together, development teams can move quickly while maintaining stronger control over the security and integrity of their software delivery pipelines.
Frequently Asked Questions About Platform Event Trap
What Is Platform Event Trap In CI/CD?
Platform Event Trap describes an event-driven security approach that automatically triggers checks when important development activities occur. These may include code commits, pull requests, dependency updates, and configuration changes. Its purpose is to identify potential risks earlier and support consistent security policy enforcement.
How Does Platform Event Trap Improve CI/CD Security?
It helps development teams detect risky changes before they progress through the software delivery process. Automated scanners can identify exposed credentials, vulnerable dependencies, and certain configuration problems. When connected to required security checks, these findings can also prevent affected changes from merging until they’re addressed.
Is Platform Event Trap The Same As A Webhook?
No. A webhook sends information when an event occurs, while Platform Event Trap describes a broader security process that may use those notifications to start scanning and enforce policies. A webhook can be part of an event-driven security system, but it doesn’t provide security analysis by itself.
Can Platform Event Trap Prevent Credential Leaks?
It can help detect exposed credentials and stop affected changes from progressing through protected workflows. However, it cannot guarantee that a credential has never been exposed. If a secret has already entered a repository or another accessible system, revocation, rotation, and investigation may still be necessary.
Does Platform Event Trap Slow Down Development?
Automated security checks can add time to CI/CD workflows, particularly when scans examine large codebases or numerous dependencies. Teams can reduce delays through incremental scanning, caching, parallel execution, and policies that focus on meaningful risks. Properly configured automation can provide useful protection without creating unnecessary disruption.
Which Platforms Support Event-Driven Security Automation?
Popular development platforms such as GitHub Actions, GitLab CI/CD, and Bitbucket Pipelines support workflows triggered by development events. Compatible security tools can integrate with these systems to perform automated scanning, report findings, and support policy enforcement.
Is Platform Event Trap Enough For Complete Pipeline Security?
No. Event-driven security automation is an important part of CI/CD protection, but it isn’t a complete security strategy. Organizations also need strong access controls, secure credentials, protected configurations, trustworthy build environments, dependency monitoring, and regular security assessments.
Learn more and explore exciting content on: HMJones.net Explained: What It Is, Who Owns It, and What It Offers



Leave a Reply